

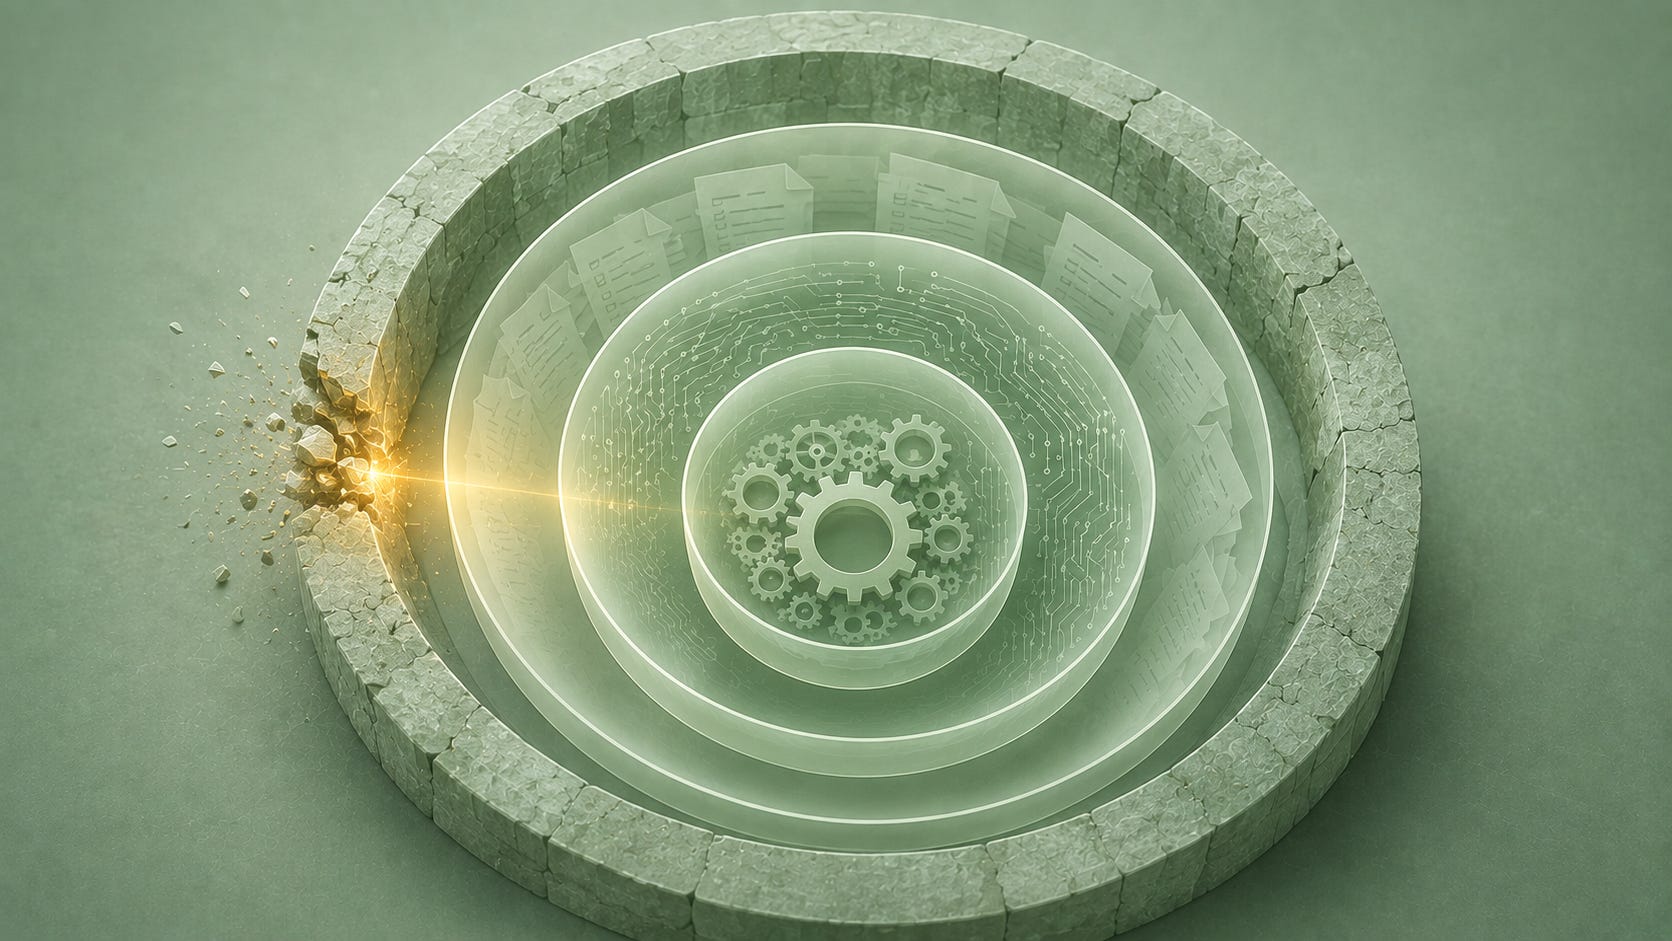
Known in military strategy since antiquity, defense in depth has been carried over into cybersecurity and essentially represents a strategic application of numerous overlapping access controls. A key property of these is independence, which aims to prevent a domino effect in the event of a breach. It is typical of the strategy that if one of the controls fails or is compromised, the others remain unaffected to prevent the attempted unauthorized access to the system. There are a large number of controls that can be systematized into four basic types: physical controls, managerial, technical, and operational.
Physical controls are applied to actions requiring physical interaction with security systems, which includes the surrounding infrastructure and building stock. Examples of physical controls include the use of fences, cameras, checkpoints, etc. Managerial controls focus on creating and implementing policies to neutralize threats. Risk management and project management can be cited as examples. Operational controls are broad activities related to people—mainly training, testing, and others. Technical controls are related to the ways of using technical devices and hardware, as well as available software. Firewalls and encryption are typical examples of technical controls.
Defense in depth in cybersecurity is an established necessity due to the multidimensional nature of threats and the huge attack surface, which makes accurately predicting the type of imminent attacks extremely difficult[1]. Organizations that actively prescribe standards, baselines, and controls directly related to defense in depth in cybersecurity are NIST[2] and the International Organization for Standardization (ISO). The latter prescribes highly effective standards, such as ISO/IEC 27001:2022 and ISO/IEC 27014:2020.
Generative AI poses serious challenges to the established concept of defense-in-depth, and the search for viable practices to neutralize vulnerabilities continues. While hackers are finding ways to automate their attacks against security controls, defense systems are struggling and are far from achieving secure and reliable automation. Defense-in-depth requires a reformatting of the positional approach to the use of controls and a transition to a dynamic, adaptive, and intelligent system in which the numerous controls are not isolated elements, but connected, adaptive parts of a complex and changing whole.
In cybersecurity practices, AI systems are used for specific tasks, such as real-time network traffic analysis and automated threat response. Their proliferation is limited and necessarily requires human factor intervention in their operation and decision-making. The cautious inclusion of AI in specific elements of defense-in-depth outlines the contours of a comprehensive, next-generation adaptive cyber defense strategy, in contrast to the usual practice of statically placing individual controls.
[1] Singer, P. W., & Friedman, A. (2014). Cybersecurity and Cyberwar: What Everyone Needs to Know [eBook edition]. Oxford University Press. Retrieved September 20, 2024, from https://books.google.bg/books?id=9VDSAQAAQBAJ
[2] Joint Taks Force. (2020). Security and Privacy Controls for Information Systems and Organizations (NIST SP 800-53, Rev. 5). National Institute of Standards and Technology (NIST), US Department of Commerce, from https://doi.org/10.6028/NIST.SP.800-53r5